
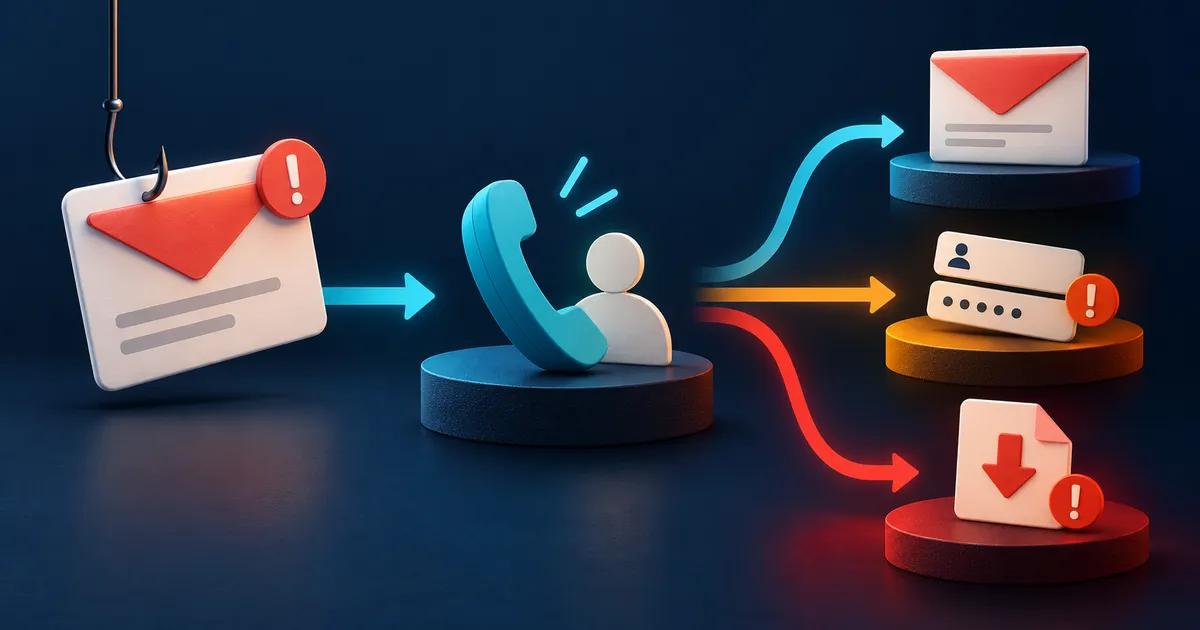
Phishing response checklist
- Pause when a message creates urgency, secrecy, fear, or unusual reward.
- Check the actual destination and sender domain without opening the link.
- Verify the request through a saved application, typed address, or known contact.
- Report through the platform so similar messages can be investigated.
- Match the response to whether you clicked, entered data, paid, or executed a file.
Separate the claim from the channel
Verification should recreate the relationship outside the message. Use a saved application, a bookmark created earlier, a telephone number from an account statement, or an established workplace channel. A reply in the same thread is weak verification because a compromised mailbox can preserve the real conversation history.
| Claim | Independent check | Unsafe shortcut |
|---|---|---|
| Account locked | Open the saved app or type the known domain | Use the alert link |
| Invoice changed | Call a known finance contact | Reply to the same thread only |
| Manager needs a gift card | Confirm through a known voice or workplace channel | Trust display name or urgency |
| Shared document | Ask the sender through an established channel | Sign in to an unfamiliar domain |
Respond according to what happened
If money, sensitive work data, or a high-risk account is involved, contact the relevant organization promptly through a verified channel.
The response grows with the action taken. A viewed message may need only reporting; submitted credentials require password and session recovery; an approved MFA prompt requires account review; a payment requires immediate contact with the financial provider; and an executed file may require device isolation and incident handling.
- No interaction: report, delete, and preserve it if policy requires.
- Clicked only: close the page, update the browser, and review downloads.
- Entered credentials: use a clean device to change the password, revoke sessions, review recovery methods, and enable strong MFA.
- Ran a file: disconnect the device and follow your incident or recovery process.
Use controls that reduce the consequence
Unique passwords, a password manager, phishing-resistant MFA where available, current software, and restricted privileges reduce the damage one message can cause. No single filter catches every targeted message.
Reduce the value of stolen information by separating passwords, using strong MFA, limiting privileges, and protecting recovery channels. Practice where session revocation and forwarding rules are reviewed before an incident. Recovery is faster when the person already knows which clean device and verified contact method to use.
How to respond to a phishing event
Do not use the message button or supplied phone number. Open the known application or type the service address from a trusted record. Check account notifications there. If the warning is absent, report the message through the mail provider and the impersonated service.
Example: an urgent account warning arrives by email
An email claims that an important account will be closed within an hour. The display name is familiar, the message includes the service logo, and the button leads to a convincing sign-in page. The urgency is the strongest signal, not proof that the claim is false or true.
Confirm recovery through a trusted channel
If credentials were entered, use a clean device to change the password, revoke sessions, review recovery methods and forwarding rules, and enable strong MFA. Preserve the original message and note what information was submitted.
Phishing response mistakes
- Looking only for spelling mistakes. Targeted messages can be grammatically correct and copied from legitimate communications.
- Calling the number printed in the suspicious message. A separate channel is useful only when its contact details come from a trusted source.
- Changing a password on a device that may have run an unknown attachment. Secure the account from a known-clean device first.
Phishing questions
Can a legitimate account be used to send phishing?
Yes. A compromised supplier, colleague, or friend can send from a real account. Verify unusual requests based on the action and context, not only the sender address.
What if I clicked but entered nothing?
Close the page, check for downloads, update the browser, and monitor the account or device. The risk is lower than credential submission but depends on what the page attempted.
Does MFA stop every phishing attack?
No. Strong MFA reduces account takeover, especially phishing-resistant methods, but attackers may steal sessions, manipulate approvals, or target recovery processes.